

Blog
Insights & updates from our experts


Resolve plant floor and IT issues before they disrupt production.

Stay audit-ready while resolving issues and reducing operational risk.
Resolve issues quickly with an AI-powered system that automates ticketing.
Unifiy IT, HR, Facilities, Finance, and more on a single, AI-powered service platform.
Simplify on-call scheduling, automate escalations, and reduce burnout.
Automate postmortems, AI summaries, and post-incident workflows
Create, organize, and continuously improve your knowledge base to find the right answers with Sera AI.
We're here to help
The integration with Atlassian Jira using the Xurrent Integration Service is
The integration with Atlassian Jira using the Xurrent Integration Service is
The integration with Atlassian Jira using the Xurrent Integration Service is
The integration with Atlassian Jira using the Xurrent Integration Service is
The integration with Atlassian Jira using the Xurrent Integration Service is
The integration with Atlassian Jira using the Xurrent Integration Service is
The integration with Atlassian Jira using the Xurrent Integration Service is
The integration with Atlassian Jira using the Xurrent Integration Service is
Resolve issues quickly with an AI-powered system that automates ticketing.
Unifiy IT, HR, Facilities, Finance, and more on a single, AI-powered service platform.
Simplify on-call scheduling, automate escalations, and reduce burnout.
Automate postmortems, AI summaries, and post-incident workflows
Create, organize, and continuously improve your knowledge base to find the right answers with Sera AI.
Resolve plant floor and IT issues before they disrupt production.
Stay audit-ready while resolving issues and reducing operational risk.

Detect, respond, and resolve incidents fast to cut downtime and MTTR.

Keep your store online, even during your biggest sales moments.
Protect patient data and resolve issues fast, so care teams stay focused on care.
Standardize service delivery across every store and channel.

We are here to help 24/7

Connect with other Xurrent Users

Get insights and tips on how to get the most out of Xurrent

Apps, APIs, and updates

Xurrent service functionality

Eliminate manual tasks, optimize workflows, and deliver faster resolutions.
Learn how organizations have reduced downtime, improved 50% MTTA & MTTR, and cut costs with Xurrent IMR.
Discover Xurrent IMR's quick support, bidirectional integrations with Jira and Slack, and more cohesive incident response capabilities compared to Opsgenie.
Understand why users value Xurrent IMR for its intuitive interface, efficient incident alerting, customizable On-call schedules, and escalations.
To make multi-factor authentication (MFA) a little easier for users, Xurrent now supports the use of hardware security keys, such as the ones provided by Yubico, Thetis and FEITIAN. A hardware security key does not rely on the user receiving a code in a text message or email so this code can be used to confirm the user’s identity. Instead, a physical key that the user owns is used as the second factor in the authentication process. Not having to wait for a code and not having to entering this code makes the whole authentication process much more convenient.
In the Xurrent Specialist Interface, users can add a security key by clicking on their picture or initials in the upper right of the browser window and selecting the ‘My Profile’ option. They can then open the ‘Access & Security’ section. That is where, if multi-factor authentication has not yet been activated, they can click on the option ‘Set up 2FA in Xurrent’.
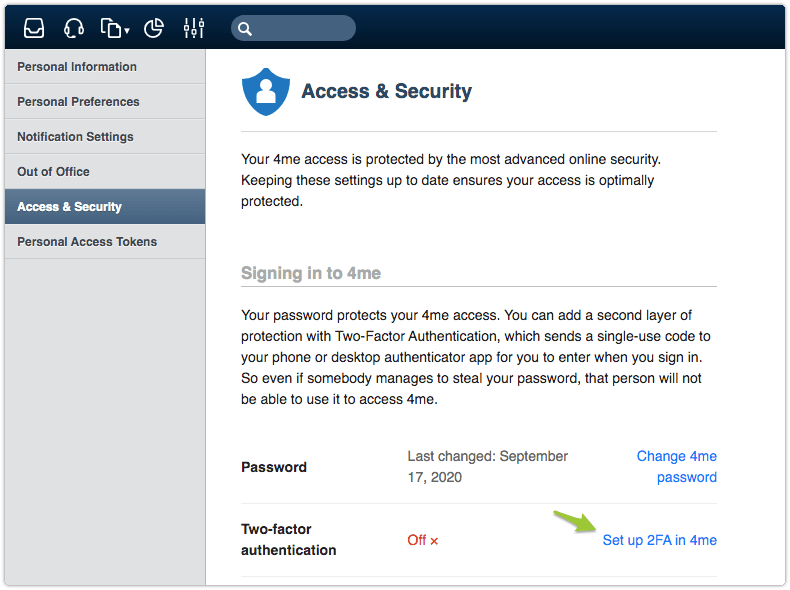
Apart from the option to set up two-factor authentication with an authentication app (like Authy or Google Authenticator), users now see the option to add a security key.
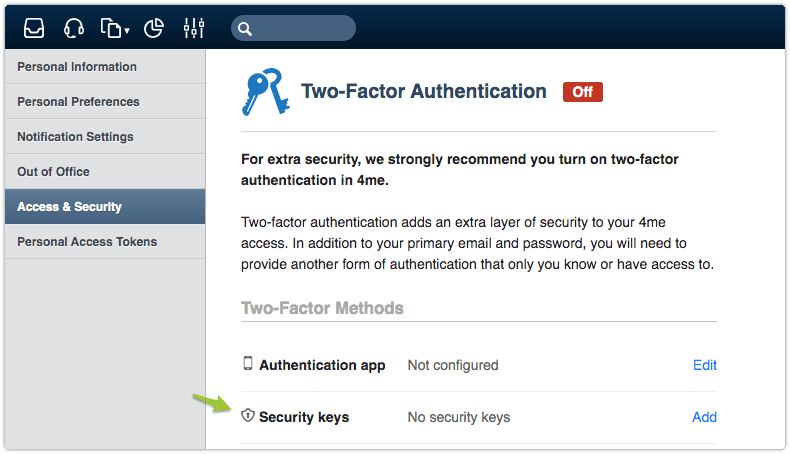
When the option to add a security key is selected, users can give their security key a name.

After pressing the Register button, Xurrent will guide them through the last steps.

Users then have the ability to download or copy a set of recovery codes before 2FA is actually activated.
After a security key has been registered, additional keys can be added, for the Xurrent App on the user’s smartphone.

The built-in TouchID sensor on MacBooks can also be added as a security key. It is even possible to use both security keys and an authentication app.
All in all, Xurrent’s support for hardware security keys gives users a lot more flexibility when they are making use of two-factor authentication to protect their Xurrent access.
Most AI SREs are pattern matchers trained on public data. They know what a memory leak looks like in the abstract. They don't know that your payments-api has a flaky liveness probe everyone ignores, that the checkout team owns the retry policy, or that the last three "database incidents" were actually cache misconfigurations. That knowledge lives in your postmortems, your Slack channels, and the heads of two senior engineers.
Most vendors will tell you ITSM implementation takes six months to a year — but modern, configuration-first platforms have rewritten the math entirely. See what real implementations look like in 2026, and why a long rollout is now a choice, not a given.